TRON API validation has changed in java-tron source merges during October 2026. Client developers should review request construction and error handling, while checking what their actual node or provider runs. The changes discussed here were merged into release_v4.8.3; that branch name is not evidence that a public service has deployed them.
This dated source review explains the practical investigation for read-only API clients and provides a tested local JSON inventory tool. It does not install a node, send oversized test traffic or change security settings. The Tronscan News homepage provides our independent explorer and record-reading guides.
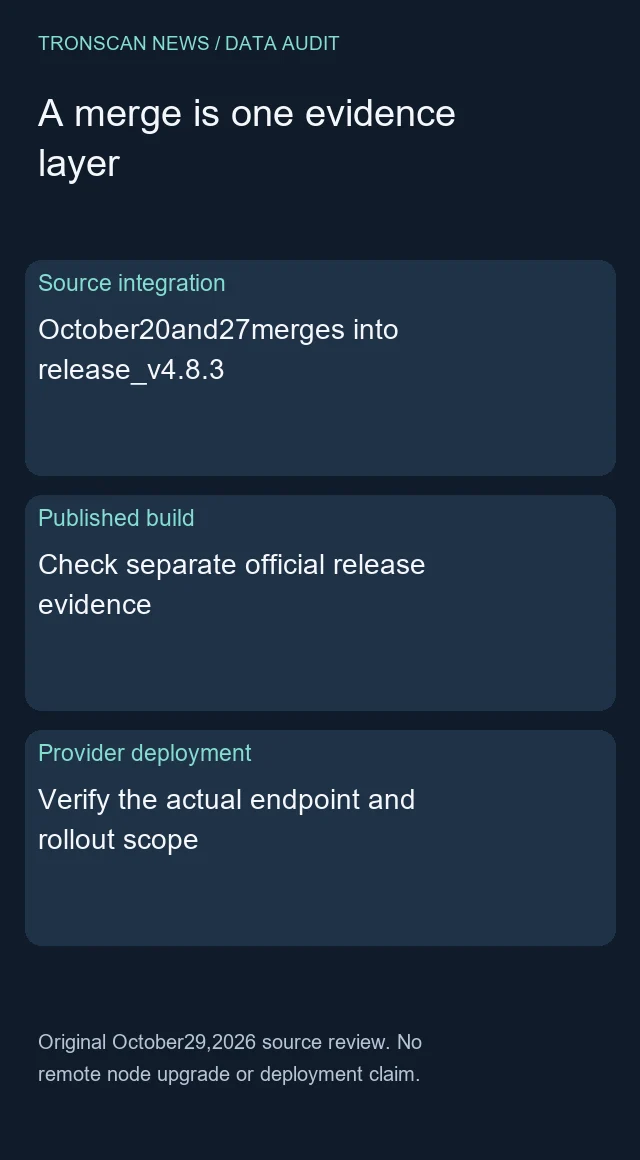
Table of Contents
1. What the October source records establish
Pull request 7052 merged on October 27 at 06:15:24 UTC. It adds pre-parse request admission across the Wallet, WalletSolidity, Database and Monitor gRPC services and the HTTP /wallet/broadcasthex route. Its limits include more than 50000 field occurrences, group-encoded fields, excessive message depth and message size. The depth limit is 32 levels, counting the root request as level one. These are request-processing changes, not a new transaction fee schedule.
The earlier pull request 7022 merged on October 20 at 04:23:19 UTC. It changes input handling, disables numeric JSON field aliases by default and can change which validation error is returned first. A previously accepted spelling or error-text assumption therefore deserves review. We checked both records on October 29; neither was merged today.
These source facts do not establish the binary version, configuration or rollout date behind a reader’s endpoint. Record those separately. Our existing TRON release-tracking article follows published release evidence; a merged pull request and a release announcement are different records.
| Evidence layer | What to retain | What it does not establish |
|---|---|---|
| Source merge | Repository, pull request, merge time and target branch | Deployment at your provider |
| Published build | Official release or build identity | Which build a remote endpoint runs |
| Endpoint observation | Host, transport, time and normal request/response | Every other endpoint’s behavior |
| Client behavior | Your request serializer and error-handling result | A consensus or transaction outcome |
2. Map TRON API validation to the interface you use
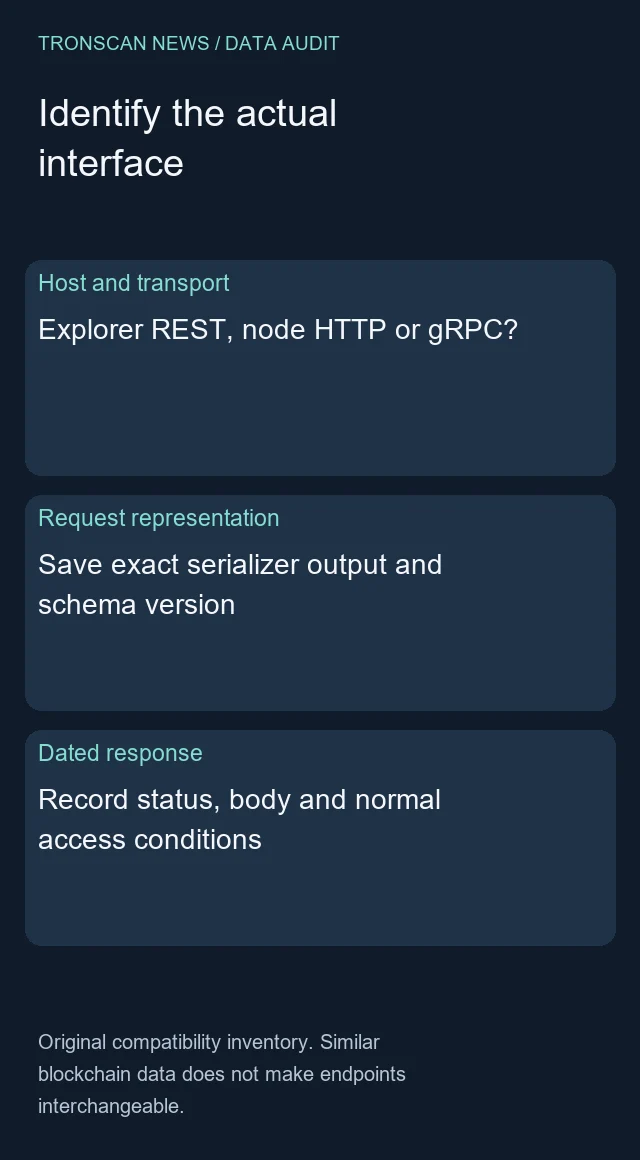
Begin with one application route rather than a general claim that “the API changed.” A website may call an explorer REST service, a node HTTP route, a gRPC method or an intermediary SDK. Those layers can expose similar blockchain data while using different request schemas and error representations.
For example, a transfer-history application built around an explorer list endpoint should first document that endpoint. It should not assume that a node gRPC admission change applies identically to its JSON request. Our read-only TRC20 transfer API guide preserves the distinction between an explorer data response and a wallet operation.
- Record the complete host and method or path for one ordinary read request.
- Identify the transport: HTTP JSON, gRPC protobuf or a documented intermediary.
- Save the actual serialized request before a library transforms or normalizes it.
- Record the schema or client-library version used to construct it.
- Capture the response status and body under that same endpoint and time context.
- Compare the observed interface with the source change’s documented scope.
This inventory does not require a stress test. A request that retrieves one known public record is enough to establish the route and representation used by your application. Compatibility boundaries that require malformed or unusually large fixtures can be investigated in an authorized local test environment, rather than probed against a shared public service.
A successful ordinary response also has a limited meaning. It shows that the recorded request worked on that occasion. It does not prove that every boundary condition is accepted or that a provider has implemented a particular merge. Avoid attaching a guessed software version to a response simply because its format looks familiar.
3. Audit saved JSON without pretending to emulate protobuf
The tool below inventories a local JSON request file. It reports byte length, a file fingerprint, numeric key paths, duplicate key paths and JSON container depth. These are useful review clues for a serializer audit. They are not the node’s protobuf field-occurrence count, message-depth calculation or admission decision.
That boundary is important. A JSON object can hide repeated keys when parsed into an ordinary dictionary. A protobuf wire message can contain occurrences that are not represented as distinct JSON keys. The admission described in the source operates on the request representation it receives; our local JSON walk measures something else.
We preserve object pairs during parsing so a duplicate key remains visible to the audit. The result lists key paths rather than copying field values into the summary. This makes a small report easier to review, although the original file still needs appropriate handling if it contains private application data.
Save the code as request_audit.py and run python request_audit.py request.json locally with Python available. It uses the standard library and sends nothing to a server. The filenames are workflow examples, not downloadable attachments hosted by this website.
import hashlib
import json
import sys


class ObjectPairs(list):
    pass


def reject_constant(value):
    raise ValueError('Nonstandard JSON constant: ' + value)


def audit_json(data):
    if not isinstance(data, bytes):
        raise ValueError('Read the original file as bytes')
    tree = json.loads(data.decode('utf-8'), object_pairs_hook=ObjectPairs,
                      parse_constant=reject_constant)
    numeric = []
    duplicates = []
    maximum_depth = 0

    def walk(value, path, depth):
        nonlocal maximum_depth
        if not isinstance(value, (ObjectPairs, list)):
            return
        maximum_depth = max(maximum_depth, depth)
        if isinstance(value, ObjectPairs):
            seen = set()
            for key, child in value:
                child_path = path + '[' + json.dumps(key) + ']'
                if key in seen:
                    duplicates.append(child_path)
                seen.add(key)
                if key and all('0' <= char <= '9' for char in key):
                    numeric.append(child_path)
                walk(child, child_path, depth + 1)
        else:
            for index, child in enumerate(value):
                walk(child, path + '[' + str(index) + ']', depth + 1)

    walk(tree, '$', 1)
    return {
        'file_bytes': len(data),
        'file_sha256': hashlib.sha256(data).hexdigest(),
        'numeric_key_paths': numeric,
        'duplicate_key_paths': duplicates,
        'json_container_depth': maximum_depth,
        'scope': 'Local JSON inventory only; not a protobuf counter or node-acceptance prediction'
    }


if __name__ == '__main__':
    with open(sys.argv[1], 'rb') as source:
        original = source.read()
    print(json.dumps(audit_json(original), indent=2))
Use the printed paths as review items. A numeric key may be an application-defined map key rather than a protobuf field alias. A duplicate key may indicate a construction bug, but this script does not know which endpoint schema the request must satisfy. It deliberately does not return an “accepted by TRON” badge.
The file fingerprint describes the exact saved bytes. It is not a transaction ID. Changing whitespace can change the file hash while leaving parsed field values equivalent. For a separate response-type question, use the TRON API integer precision comparison, checked November 2, 2026. A local request inventory does not restore digits already lost while parsing a response.
4. Reproduce our local audit fixtures
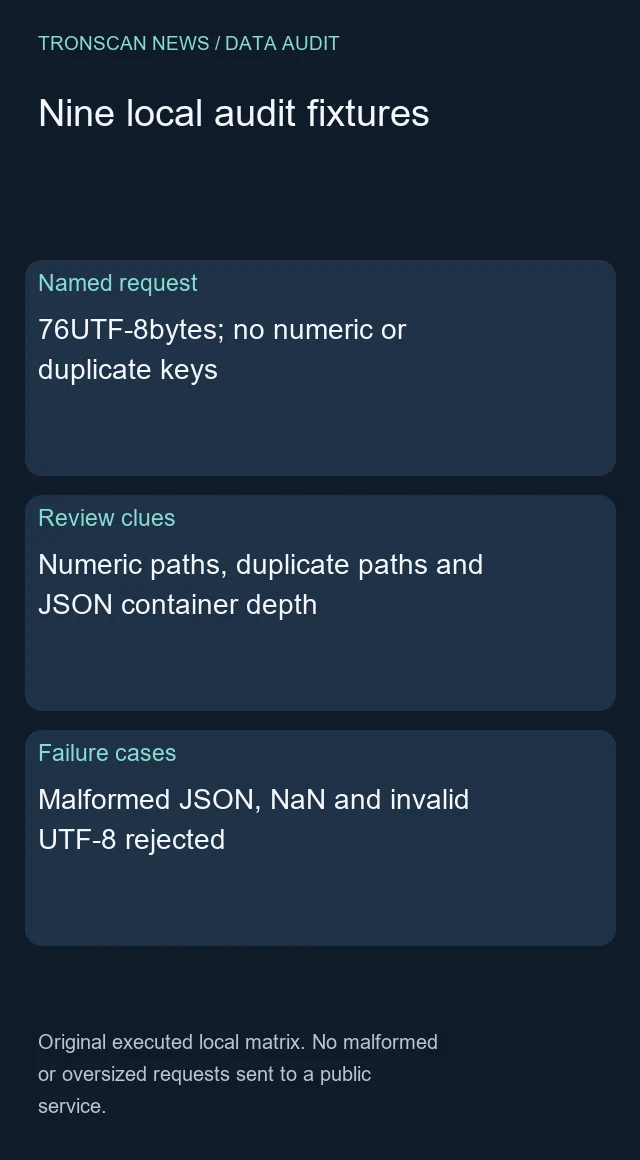
We executed nine small local cases. The named-request fixture used {"value":"530fe4aa80f9427cb25a469abc5ebb08230db6dff8adcb97ce0ec895d3ad4a8e"}, encoded as a UTF-8 byte string with no trailing newline. The audit measured 76 bytes, no numeric key paths, no duplicate key paths and a container depth of one.
The identifier came from a retained public transaction body, but this fixture was only inventoried locally. We did not submit it as part of a before-and-after node upgrade test. Its normal field spelling gives a reviewable starting point for the JSON tool, not evidence about rollout status.
| Local fixture | Measured or expected result | Review purpose |
|---|---|---|
| Named value request | 76 bytes; no flagged key paths | Positive inventory case |
| Numeric key “1” | Path $[“1”] reported | Locate a spelling worth schema review |
| Two value keys in one object | Duplicate value path reported | Preserve ambiguity before dictionary normalization |
| Object containing an array and object | JSON container depth 3 | Test our declared local depth metric |
| String value “1” under a named key | No numeric key flagged | Distinguish a value from a field name |
| Array-root fixture with numeric key | Indexed path reported | Keep location within the input visible |
| Malformed JSON | Rejected | Do not audit a partially parsed file |
| Nonstandard NaN constant | Rejected | Do not silently accept nonstandard JSON |
| Invalid UTF-8 byte | Rejected | Make text-decoding failure explicit |
These cases establish the displayed tool’s behavior on the named inputs. We did not run the java-tron unit suite, benchmark a node, count all historical transactions or test production capacity. Source authors’ reported tests are their evidence; our executed fixtures are a different, much narrower test set.
Do not compare our depth-three result directly with a protobuf limit. The structures and counting rules differ. Likewise, a small file can contain an unusual representation, and a large file can be valid for a different interface. Size, JSON structure and schema conformance answer separate questions.
5. Review error handling by category and context
The admission merge documents INVALID_ARGUMENT for its invalid-input paths and RESOURCE_EXHAUSTED for oversized compressed requests. It also describes more specific rejection handling rather than reaching the business method. These details should be checked against the actual transport and deployed implementation before changing a client.
The official gRPC status-code guide distinguishes invalid arguments, exhausted resources and unavailable services. Those categories are not interchangeable. Preserve both the machine-readable status and the accompanying description; do not classify every failure by searching for one historical English error string.
For a client investigation, first ask whether the saved request could be decoded and whether it matched the documented schema. Then consider provider access limits and availability. A response saying the request was rejected does not establish that the underlying public transaction is absent from the chain.
For read-only requests, a bounded retry after a genuinely temporary service error may be appropriate under the provider’s policy. Repeating an unchanged malformed request is not a correction. Keep retry policy separate from transaction-submission logic: a network timeout during a state-changing operation requires its own status reconciliation, outside this local audit.
| Observed problem | First evidence to retain | Do not infer |
|---|---|---|
| Local JSON parsing fails | Original file and exact decoding error | A node rejected the request |
| Endpoint rejects an input | Host, method, serialized input and status | The blockchain record does not exist |
| Provider limits access | Provider response, time and normal access policy | All nodes have identical limits |
| Old error text changes | Code and structured response fields | Every business outcome changed |
| Ordinary request succeeds | Exact request and dated response | All boundary cases passed |
6. Keep the migration comparison attributable
Choose one client behavior to investigate at a time. For example, review whether a request builder emits documented field names rather than relying on an accidental alias. Save its original output, make the smallest justified change in your own authorized codebase, and compare the serialized request again before testing the normal read workflow.
Do not modify an endpoint’s configuration merely to make an old fixture pass. If a provider exposes a compatibility policy, document it and adapt to the supported interface. An application-level migration review should not quietly weaken validation or turn a production service into a test target.
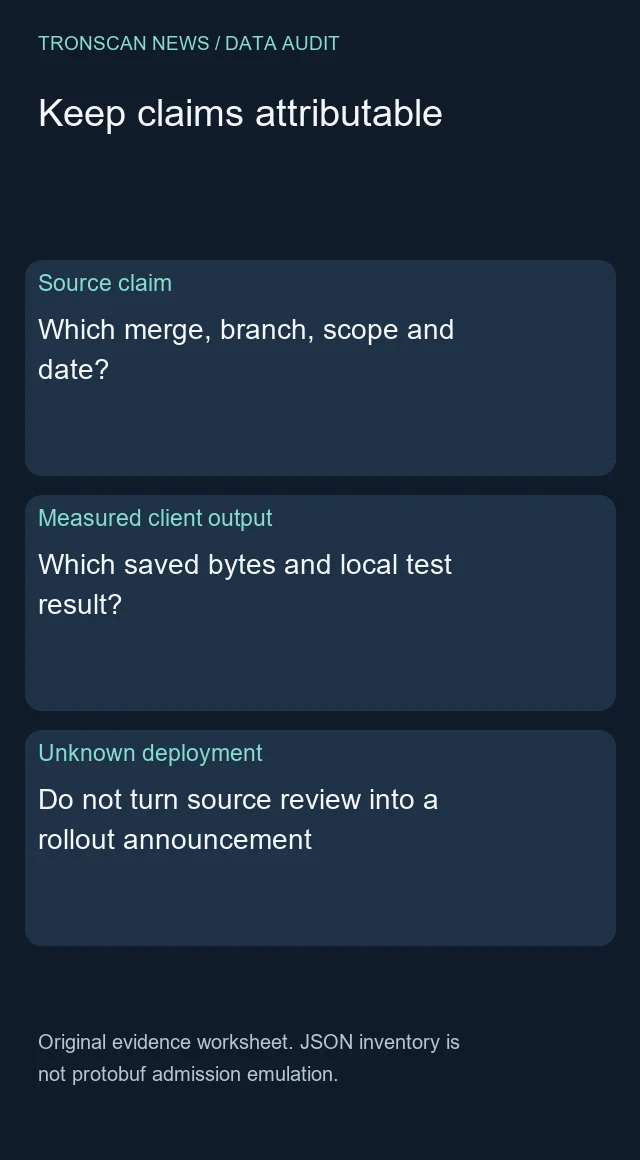
A useful comparison note has three sections: the source claim, your measured client output and the deployment evidence that remains unknown. That structure makes it possible to revise the conclusion when a provider later announces a rollout, without rewriting an earlier source merge as a launch that had already happened.
Keep a normal positive request in the test set. A review consisting only of malformed cases can demonstrate rejection while failing to show that the application’s intended read path still works. Conversely, one positive response cannot establish boundary handling. State which category was actually tested.
When multiple errors appear possible, do not assume their order is a public contract unless the endpoint documents that guarantee. Changing which validation happens first can alter a response without changing the underlying input defect. A robust client records enough structured evidence for diagnosis rather than making a recovery decision from a single message fragment.
7. Read the audit output as a review worksheet
Our 17-byte numeric-key fixture was {"1":"synthetic"}. The output located $["1"]. That path says where the key appeared; it does not say that the node resolved it as an alias. To investigate an application, identify the request type and compare the field spelling with its documented schema before deciding what needs to change.
The 34-byte duplicate fixture was {"value":"first","value":"second"}. The audit reported $["value"] as duplicated. Keeping this clue matters because converting the object immediately to a normal dictionary can discard evidence of how the request was originally written. The correct fix belongs in the serializer or caller that created the ambiguous request, after confirming the intended value.
The nested fixture was {"items":[{"2":5}]}. It measured 19 bytes, with JSON container depth three and numeric path $["items"][0]["2"]. The path preserves both the named object member and array index. A flat list of flagged key names would lose that location and make it harder to identify which part of a larger request requires review.
| Measured fixture | Bytes | JSON container depth | Interpretation |
|---|---|---|---|
| Named value request | 76 | 1 | One top-level object |
| Numeric key | 17 | 1 | A key path to review |
| Duplicate value key | 34 | 1 | Two occurrences preserved in the local parse |
| Nested object and array | 19 | 3 | Our JSON metric, not a protocol nesting result |
| String value containing a digit | 13 | 1 | A numeric-looking value is not a numeric field name |
| Array-root example | 9 | 2 | Inventory works, while endpoint validity remains unknown |
Notice the last distinction: this utility can inventory an array-root document without establishing that an endpoint accepts an array as its request. A clean report means only that the particular review clues were absent. It does not validate required fields, address formats, numeric ranges, authentication or contract-specific semantics.
For a small regression record, keep the original request file, this output and the serializer version together. If a code change removes a duplicate or changes a field name, describe that concrete difference. Do not report a compatibility improvement solely because the file became shorter or its fingerprint changed.
Finally, retain a boundary statement with any shared audit output: local JSON inventory completed, deployment not verified, and no production rejection test performed. That wording lets another engineer reuse the measured file facts without accidentally promoting them into a broader rollout or security claim.
The command does not choose a pass/fail policy for your application. A normal process exit means the JSON inventory ran; numeric or duplicate paths can still be present in its output. If you integrate the utility into a build check, inspect the named arrays and decide which findings your documented schema permits. Treat a parsing exception separately from a completed inventory that contains review items. That prevents an exit-status-only check from turning a reported duplicate into an unnoticed green result. Keep this local review policy distinct from any statement about what a deployed node will accept.
Frequently asked questions
Does the release_v4.8.3 branch name prove my provider upgraded?
No. A target branch identifies source integration. Verify the provider’s build and deployment evidence separately; this review did not inspect or upgrade a remote node.
Does this change mean every explorer HTTP API has the same limits?
No. Identify the actual endpoint and transport. An explorer REST service, node HTTP route and gRPC service are separate interfaces unless their documentation establishes a shared policy.
Can the JSON audit predict whether a node accepts my request?
No. It inventories local JSON bytes and key paths. It is not a protobuf scanner, endpoint-schema validator or implementation of the node’s admission guard.
Should an unchanged invalid request be retried repeatedly?
No. Preserve the response and correct the identified input issue through the documented interface. Treat temporary service availability and provider quotas as separate cases with their own bounded handling.
Were the malformed fixtures tested on Mainnet?
No. All nine audit fixtures ran locally. We did not submit malformed or oversized traffic to a public node, sign a transaction or measure production throughput.
Source review checked October 29, 2026 by the Tronscan News editorial team. AI assisted drafting; the displayed local JSON tool and nine fixtures were executed. This independent publication is not an official TRON or TRONSCAN release channel. Report reproducible corrections through this page’s comments with the affected step and public source; omit credentials and signing secrets.
Leave a Reply